Four controls.
One protected
cloud estate.
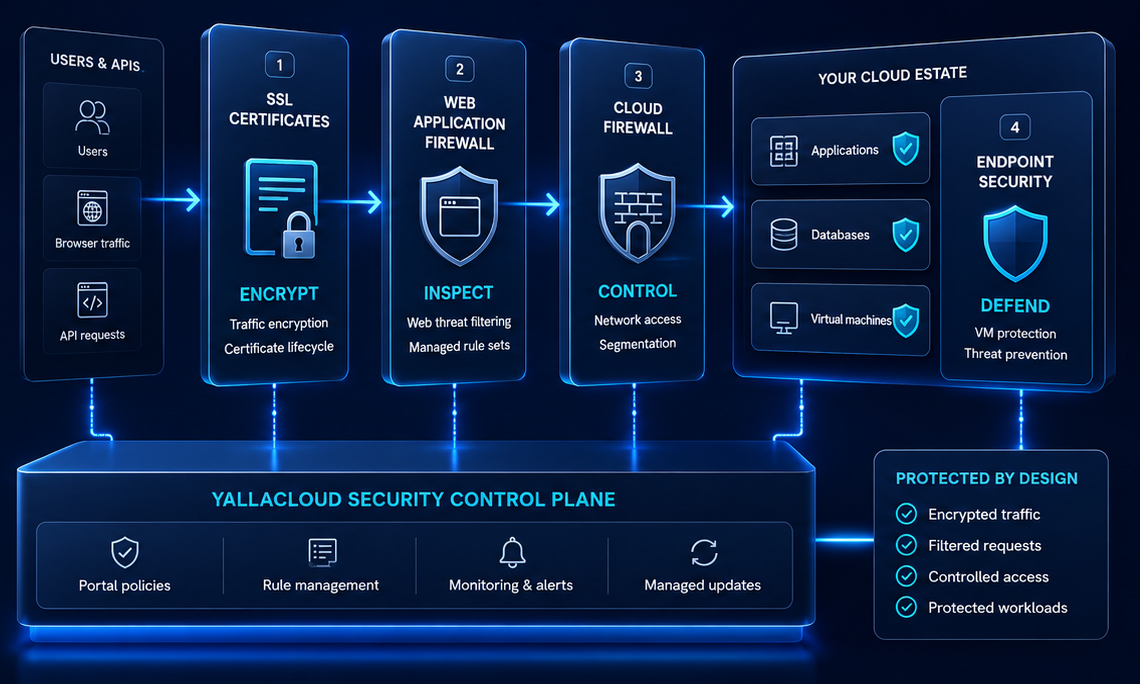
Encrypt traffic, filter application threats, control network access and protect every workload with SSL certificates, WAF, cloud firewalls and endpoint security — configured from one portal and operated as part of your cloud.
Controls at every layer.
Transport, application, network and endpoint — four controls that report to one SOC, so an alert anywhere becomes action everywhere.
 Auto-renewal
SSL
Certificate lifecycle without the expiry-day panic — issued, renewed and monitored for you.
 Managed rules
WAF
Managed web application firewall in front of your apps — rules tuned by analysts, not defaults.
 Policy-as-code
Firewalls
Network firewalls and micro-segmentation managed as code — a rulebase you can actually read.
 EDR
Endpoint Security
EDR across servers and workspaces — behavioural detection with a SOC that acts on what it sees.
One SOC behind every control.
Four controls, one security operations centre — the same analysts tune the WAF, read the EDR alerts and guard the platform itself.
Make secure the default, not the project.
Controls arrive as platform features — switched on with the estate, not bolted on after the first audit finding.
Three layers between the internet and your data.
Traffic meets the WAF and terminates TLS at the edge, crosses read-able firewall policy at every boundary, and lands on endpoints watched by EDR. Each layer reports to the same SOC — so one anomaly anywhere is context everywhere.
Which control stops which threat?
The four layers overlap on purpose. Start where your exposure is — most estates end up with all four.
Make secure the default, not the project.
Bring your current controls — the SOC team will map them to the four layers, close the gaps and take the watch.
Gap assessment before any commitment