Platform/Networking/Virtual Networks

Segmentation as code, not as tribal knowledge.

Isolated software-defined networks with routing, peering and full change history — the network map finally matches reality.

VPC-style isolationCross-region peeringChange history
Capabilities

Networks you can reason about

Built for performance, security and control so you can connect with confidence.
Isolated by design
Private address space per network with explicit, auditable paths between them.
Boundaries with teeth  →
Routing & peering
Cross-network and cross-region peering managed as code.
Paths you choose  →
Security groups
Stateful rules at the workload boundary, versioned like code.
Least privilege inbound →
Flow visibility
Flow logs feed Obersva and the SOC for real east-west visibility.
Flows logged, queryable →
Terraform-native
Networks, subnets and rules managed as code.
Diagrams that deploy →
Free east-west
No charge on traffic across your own networks.
Architecture without a meter →
NAT & egress control
Managed NAT with explicit egress policies.
Outbound on your terms →
Multi-zone spans
Networks stretch across zones where designs need it.
One network, two zones →
Service endpoints
Managed databases and storage attach privately.
PaaS without public paths →
DHCP & IPAM tied in
Addressing integrates with Virtue Suite records.
The plan stays true →
Resilient by designBuilt to continue, even when hardware fails.
Predictable performanceConsistent I/O for the apps that matter.
Efficient at scaleOne flat fee. Scale without waste.
Backed by humansReal experts. Real support. Every time.
Compare the fabrics

Three fabrics, one estate

Private networks carry no ingress or egress charge in either direction. The difference between the fabrics is how much control you hold over what talks to what.

ProductionEdgeComing soon
FABRIC 01
Base SDN
Direct internet, security groups

Instances sit on a shared internet-facing fabric where security groups decide what reaches them — nothing to design, just the ports you allow.

Best for
Single-tier workloadsDev & testPublic services
Where it runs
Dubai AZ1Dubai AZ2RiyadhBahrainMumbaiSingaporeAbu DhabiMilanFrankfurtNairobi
FABRIC 02
Advanced SDN
Your own private networks

A distributed-switch model: create your own private networks, put virtual firewalls in front of them and decide exactly how public and private segments connect.

Best for
Multi-tier applicationsSegmented environmentsFirewalled workloads
Where it runs
Dubai AZ1Dubai AZ2RiyadhBahrainMumbaiAbu DhabiFrankfurtNairobi
FABRIC 03Most capable
VPC SDN
Many networks, many platforms

One private VPC spanning CloudStack, VMware and Kubernetes, with your own firewalls in front and as many private networks inside as you need — multi-tenancy included.

Best for
Multi-platform estatesMulti-tenant hostingRegulated segmentation
Where it runs
Dubai AZ1RiyadhBahrainMumbaiDubai AZ2Nairobi
Two ways to run it

Self-service, or network operations

Both sit inside the flat fee. The difference is who makes the change.
Self-serviceYou hold the consoleYour team creates networks, subnets and rules through console, API or Terraform inside agreed guardrails.
Full API and Terraform control
Change history on every rule
Quotas instead of tickets
Best for:Platform and network teams
Explore Self-service plans
OR
Network OperationsWe hold the pagerOur engineers design and execute changes to a reviewed standard, keeping topology documentation current.
Reviewed, reversible change process
Topology and IP documentation maintained
24/7 monitoring of paths and routes
Best when:The network cannot be a side job
Explore Network Operations plans
Who decides, who runs it

What each group gets from Virtual Networks

Four groups shape a cloud decision. Pick the one you belong to — the platform reads differently from each seat.

Isolation is a design, not a hope

Environments and entities are separated by construction, which makes both risk conversations and audits shorter.

GovernedSovereignPredictable

FAQs

How many networks can we create?
As many as your design needs — they are software-defined, so the limit is governance rather than hardware.
Is traffic between networks charged?
No. Private networks are free in both directions — no ingress or egress charge on traffic across your own estate.
Which fabric should we start on?
Base SDN if a security group is enough. Advanced SDN when you want your own private networks and firewalls. VPC SDN when workloads span CloudStack, VMware and Kubernetes, or when you need multi-tenancy.
Can we manage this as code?
Yes — Terraform, CLI and API cover networks, subnets, routes and rules natively.
How do we reach our own datacentre?
Privately, through CloudConnect or DirectConnect, with BGP routing into your existing address plan.
Who keeps the address plan?
IPAM through Virtue Suite, so allocations are planned and auditable instead of living in a spreadsheet.
How is the flat fee different from public cloud pricing?
Everything inside the plan you opt for is included — no additional charge for the components that make it up. Public clouds meter each component on consumption, so the bill moves with usage. Here the plan is reserved for you and the figure you agreed is the figure you pay.
How do limits and quotas work?
Quotas are yours to shape — carve capacity per team or project and delegate inside it. Hard ceilings are a conversation, not a wall; the estate re-baselines at thresholds you approve.
Can security services be included in my plan?
Yes. Endpoint security, firewalls and WAF are scoped into the same flat fee when you add them — one figure, no separate security invoice.
Better together

Build more around every network.

Connect Virtual Networks to the compute, addressing, security and visibility services that turn isolated resources into a controlled cloud environment.

At the core
Virtual Networks

Software-defined networking becomes a complete environment when traffic, addressing, security and governance work as one.
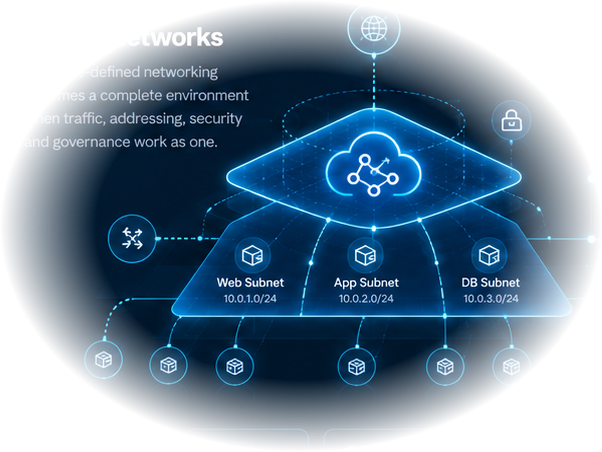
SegmentRouteSecureObserve
One connected network
ComputeAddressingRoutingSecurityGovernance
Noura
Noura — AI Cloud Experience Guide

Two ways Noura gets you moving

Choose the way that fits you best — Noura makes every step simple.
Not sure where to start?
Start the conversation

Describe the workload in plain language — Noura works out the tiers, sizes and protection with you.
Plain language input
Smart sizing & protection
No commitment. Just clarity.
Talk to Noura
Want to see it working?
Experience it in the marketplace

Explore CloudSouq experiences built on these services — see Virtual Networks working inside real solutions before you commit to anything.

Try real solutions
See it work in action
Commit with confidence
Explore CloudSouq
Noura is your guide at every stepfrom first question to final success.Intelligent
Guidance
Secure &
Trusted
Human
Simplicity