Segmentation enforced, changes accountable.
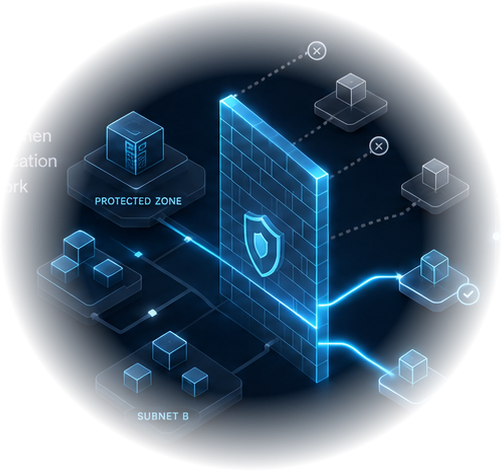
Network firewalls and micro-segmentation delivered with our partners OPNsense, Sophos and Fortinet — every rule reviewed, every change reversible, every path explicit.
The rulebase, under control
Centralised control. Consistent enforcement. Smarter decisions, everywhere.
Partnered with OPNsense, Sophos and Fortinet
Network firewalls are delivered on platforms from our security partners — deployed as dedicated instances inside your tenancy, managed as code and watched by the SOC and NOC around the clock.
Dedicated OPNsense instances with a fully open rulebase — every rule inspectable, exportable and driven as code through the API, with no per-feature licensing.
Sophos Firewall brings IPS, TLS inspection and application control to the boundary, with reporting clear enough to hand straight to an auditor.
FortiGate NGFWs enforce from the perimeter to east-west micro-segmentation — identity-aware policy at line rate for the largest regulated estates.
You hold the rulebase, or we do
Both keep every change reviewed and reversible. The difference is who makes it.
 Self-managed RulesYou hold the policyYour team writes and reviews policy through the console or as code, with history on every change.
 Managed FirewallWe hold the policySecurity Operations owns the rulebase, executes your change requests and reviews the policy set on a cycle.
What each group gets from Firewalls
Four groups shape a cloud decision. Pick the one you belong to — the platform reads differently from each seat.
Segmentation limits how far an incident can travel, which changes the shape of the risk conversation entirely.
FAQs
Build more around every network boundary.
Connect Firewalls to the platform services that turn segmentation and policy into a complete security posture.
Network controls become a complete security plane when workloads, delivery, application defence and evidence work around them.
Two ways Noura gets you moving
Choose the way that fits you best — Noura makes every step simple.
Describe the workload in plain language — Noura works out the tiers, sizes and protection with you.
Explore CloudSouq experiences built on these services — see Firewalls working inside real solutions before you commit to anything.
GuidanceSecure &
TrustedHuman
Simplicity