Platform/Containers/Managed Kubernetes

Clusters you use. Not clusters you nurse.

CNCF-conformant Kubernetes with the control plane patched, upgraded and watched by us — your team keeps kubectl, loses the 2am pages.

CNCF-conformantPatched for youGPU node pools
Capabilities

Upstream Kubernetes, operated

Enterprise Kubernetes without the complexity. We run the control plane so you can ship faster.
Conformant clusters
Upstream Kubernetes — no forks, no proprietary lock-in, standard tooling.
No forks, no lock-in  →
Control plane, ours
Patching, upgrades and etcd health are our pager, not yours.
etcd is our 2am problem  →
Batteries included
Integrated registry, load balancers, storage classes and ingress.
Registry, ingress, storage →
GPU node pools
Schedule AI workloads onto GPU pools inside the same cluster.
AI on the same cluster →
Cluster autoscaling
Node pools grow and shrink with demand between agreed bounds.
Capacity follows pods →
Policy baselines
Admission policies and pod security enforced from day one.
Governed by default →
Private clusters
API server and nodes on your networks — no public control plane.
The cluster stays inside →
Upgrade cadence
Tested version steps with rollback plans, scheduled with you.
Current without breakage →
Workload backup
Cluster state and persistent volumes protected with restore drills.
Stateful without fear →
Terraform-native
Clusters, pools and add-ons managed as code.
Clusters from the pipeline →
Resilient by designBuilt to continue, even when hardware fails.
Predictable performanceConsistent I/O for the apps that matter.
Efficient at scaleOne flat fee. Scale without waste.
Backed by humansReal experts. Real support. Every time.
Compare the clusters

Shared, dedicated, or accelerated

Upstream Kubernetes in all three — the difference is how isolated the nodes are and what they are built to run.

ProductionEdgeComing soon
TIER 01Start here
Standard Cluster
The everyday platform

A conformant cluster with a managed, patched control plane and autoscaling worker pools — enough for most teams shipping services daily.

Best for
MicroservicesInternal platformsDev & test
Where it runs
Dubai AZ1Dubai AZ2RiyadhBahrainMumbaiAbu DhabiFrankfurtNairobi
TIER 02
Dedicated Cluster
Isolated nodes, your rules

Worker nodes on dedicated hosts inside your own boundary, for regulated workloads and tenancy separation you must be able to prove.

Best for
Regulated servicesMulti-entity tenancyProduction platforms
Where it runs
Dubai AZ1RiyadhBahrainMumbaiDubai AZ2Nairobi
TIER 03
GPU Cluster
Scheduled accelerators

GPU node pools attached to the same cluster so training and inference queue alongside your application workloads.

Best for
Model trainingBatch inferenceAI platforms
Where it runs
Dubai AZ1RiyadhMumbaiLagosNairobi
Two ways to run it

You operate the workloads, or we do

The control plane is managed either way. The question is who owns what runs on it.
Platform OnlyYou hold kubectlWe keep the control plane patched, upgraded and monitored; your team owns the manifests and the release cadence.
Full cluster-admin where it matters
Version upgrades planned with you
No 2am control-plane pages
Best for:Teams with platform engineers
Explore Platform Only plans
OR
Operated PlatformWe hold the pagerCloud Operations runs ingress, observability, policy and upgrades to an agreed standard, with your team shipping into it.
Golden baseline: ingress, logging, policy
24/7 monitoring of cluster and workloads
Upgrade and patch cycles executed for you
Best when:Kubernetes cannot be a side job
Explore Operated Platform plans
Who decides, who runs it

What each group gets from Managed Kubernetes

Four groups shape a cloud decision. Pick the one you belong to — the platform reads differently from each seat.
Modernisation without a platform team hire

A conformant, supported Kubernetes estate in-country, so container strategy does not wait on recruitment.

GovernedSovereignPredictable

FAQs

Is this upstream Kubernetes?
Yes — CNCF-conformant, so standard manifests, Helm charts and operators work without vendor-specific rewrites.
Who handles upgrades?
We do, on a cadence agreed with you, with a tested path and a rollback plan for each version step.
Can we get cluster-admin?
Yes. Your team keeps the access it needs; we retain the control-plane responsibilities we are on the hook for.
Can GPU workloads share the cluster?
Yes — GPU node pools attach to the same cluster with the device plugin and scheduling managed for you.
How does it connect to our databases?
Privately, over your virtual networks — managed databases and clusters live on the same fabric with no egress charge between them.
How is the flat fee different from public cloud pricing?
Everything inside the plan you opt for is included — no additional charge for the components that make it up. Public clouds meter each component on consumption, so the bill moves with usage. Here the plan is reserved for you and the figure you agreed is the figure you pay.
Can we drive it from Terraform and CI?
Yes. Every operation is exposed through the REST API, CLI and a maintained Terraform provider, with scoped API keys per team. If the console can do it, your pipeline can do it.
How do limits and quotas work?
Quotas are yours to shape — carve capacity per team or project and delegate inside it. Hard ceilings are a conversation, not a wall; the estate re-baselines at thresholds you approve.
Can security services be included in my plan?
Yes. Endpoint security, firewalls and WAF are scoped into the same flat fee when you add them — one figure, no separate security invoice.
Better together

Build more around every cluster.

Connect Managed Kubernetes to the compute, storage, data, networking and governance services cloud-native applications depend on.

At the core
Managed Kubernetes

Managed orchestration becomes a complete application platform when compute, data, traffic, visibility and governance work as one.
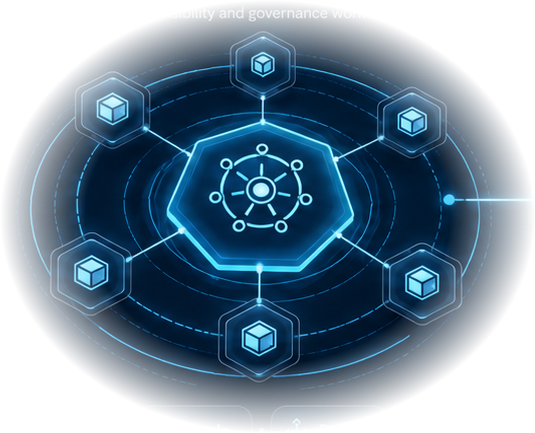
DeployScaleBalanceGovern
One application platform
ComputeDataTrafficVisibilityCompliance
Noura
Noura — AI Cloud Experience Guide

Two ways Noura gets you moving

Choose the way that fits you best — Noura makes every step simple.
Not sure where to start?
Start the conversation

Describe the workload in plain language — Noura works out the tiers, sizes and protection with you.
Plain language input
Smart sizing & protection
No commitment. Just clarity.
Talk to Noura
Want to see it working?
Experience it in the marketplace

Explore CloudSouq experiences built on these services — see Managed Kubernetes working inside real solutions before you commit to anything.

Try real solutions
See it work in action
Commit with confidence
Explore CloudSouq
Noura is your guide at every stepfrom first question to final success.Intelligent
Guidance
Secure &
Trusted
Human
Simplicity